

Identity, Access Control & SSO with Keycloak
Stop rebuilding login
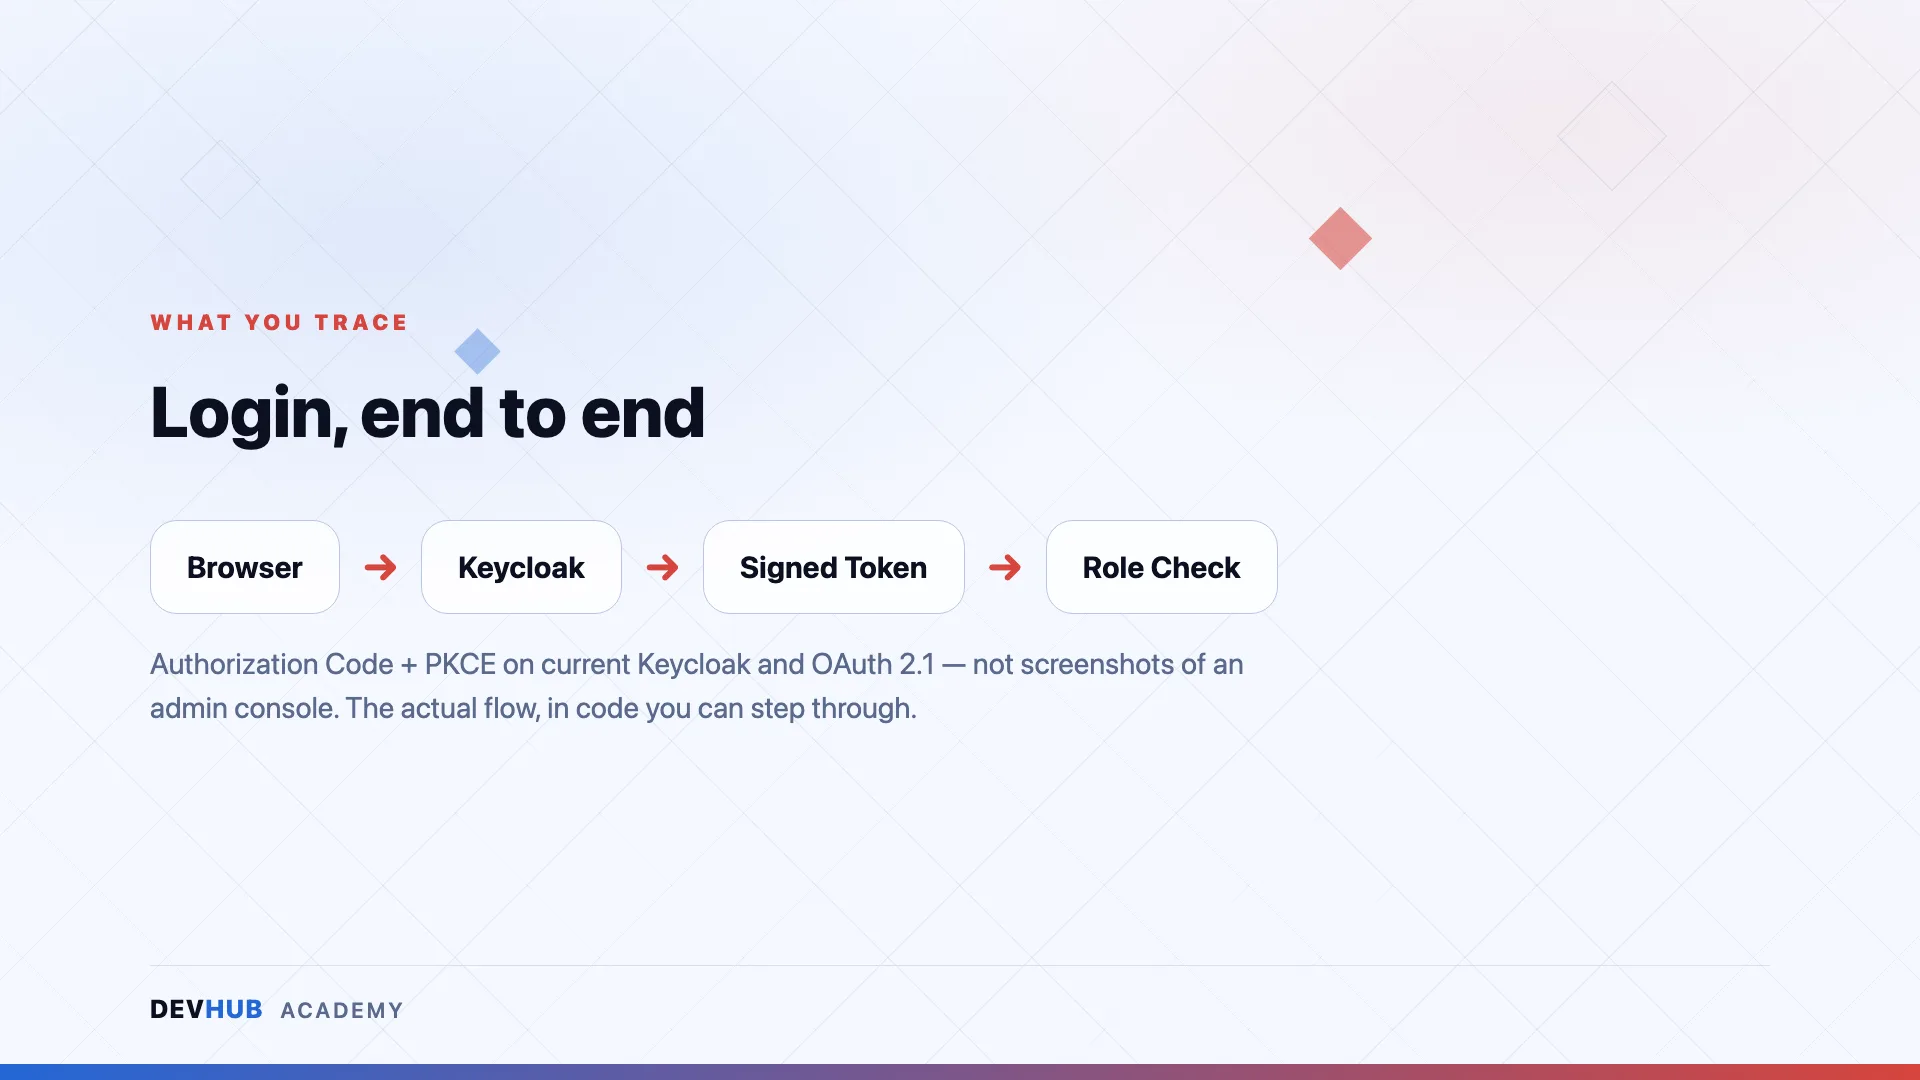
For developers and tech leads who keep rebuilding login, roles, and password resets in every app. You leave able to run central identity for any stack — and to trace a login from browser redirect to signed token to role check.
The problem
Sound familiar?
You’ve built login from scratch four times. Every app has its own users table, its own reset flow, its own place to forget to disable a leaver’s account.
“Just use Keycloak” — but the docs show you screens, not the flow, so you copy config you can’t debug.
SSO looks like magic until it breaks, and then nobody on the team can explain the three sessions in play.
Your API “checks the token” with a library you couldn’t defend in a security review.
What you leave with
What you walk away with
Not notes — artifacts you built yourself, ready to use on Monday.
Keycloak running in Docker and a training realm you modelled yourself — clients, users, groups, roles
A web app wired to Keycloak with Authorization Code + PKCE login
An API that enforces bearer tokens with real 401/403 role checks
SSO across two apps from a single login — and single logout done correctly
A brokered login from a second identity provider, a realm backup you restored, and a hardening checklist applied to your realm
The proof
Why this course delivers
2
apps on SSO from one login
OAuth 2.1
current flows — PKCE, no legacy
100%
hands-on, zero real user data
Taught by a trainer running Keycloak-based SSO and central identity in production on a university-scale IAM platform
Every lab ends with a request you can trace end to end: browser redirect → signed token → role check
Built on current Keycloak and OAuth 2.1 — Authorization Code + PKCE, not deprecated flows
100% hands-on on your laptop — nothing runs on real user data
Questions
Frequently asked
Who is Identity, Access Control & SSO with Keycloak for?
For developers and tech leads who keep rebuilding login, roles, and password resets in every app. You leave able to run central identity for any stack — and to trace a login from browser redirect to signed token to role check.
What do I walk away with?
Artifacts you built yourself, not notes — including:
- Keycloak running in Docker and a training realm you modelled yourself — clients, users, groups, roles
- A web app wired to Keycloak with Authorization Code + PKCE login
- An API that enforces bearer tokens with real 401/403 role checks
Is this training hands-on or lecture-based?
Hands-on. Our trainings are taught by practitioners who ship production software daily — you spend the sessions building, breaking and fixing real things, not watching slides.
Is it delivered online or in person?
Delivery format and duration are decided per run — some runs are physical, some online. The details for each scheduled session are announced when registration opens.
How do I register, and how much does it cost?
Dates, venues and pricing are announced with each run. Hit “Get Notified” and you’ll be first in line when registration opens.
Ready to take a seat?
No run scheduled yet? Get notified and be first in line when registration opens — dates, venue and pricing land in your inbox first.